Stopping Brute Force on a PHP Login Without Redis
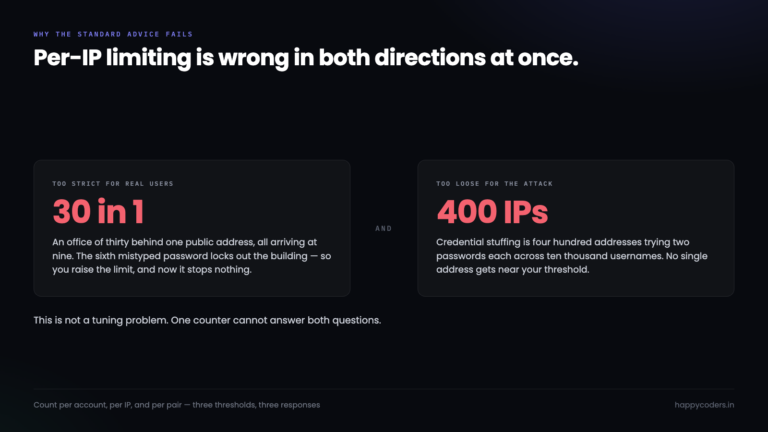
The most common attack a small site actually sees, and the fix most tutorials get wrong: a per-IP limit locks out a whole office behind one NAT and misses the attack it was built for. A database-backed limiter that does neither.
Read article